In this article
Splunk Overview & 2026 Industry Position
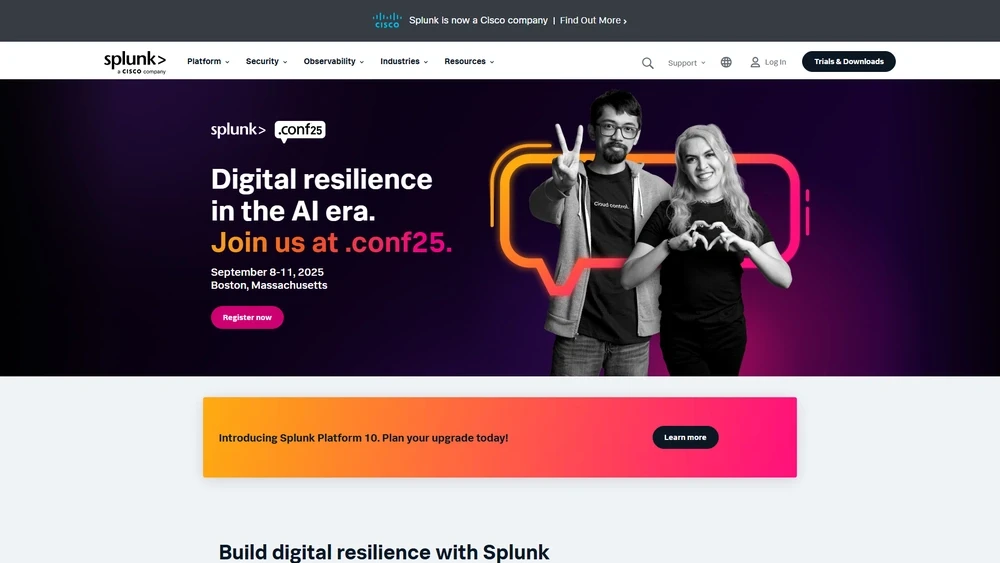
Splunk has long been recognized as a leader in operational intelligence, empowering businesses to analyze machine-generated data for insights and action. In 2026, the company doubles down on its foundational promise: turning data into doing. As enterprises demand resilient, secure, and agile infrastructure, Splunk operates at the nexus of observability, security, and centralized data analytics. Its positioning this year emphasizes AI-powered tooling, end-to-end integrations, and real-time monitoring — catering to Fortune 500s, public sector organizations, and tech-forward mid-market companies.
From Launch to 2026: Splunk’s Journey
Founded in 2003, Splunk began as a search engine for log data, enabling system admins to troubleshoot issues faster. Key milestones mark its evolution:
- 2006: Splunk 1.0 launches as a downloadable platform for log analysis.
- 2012: IPO raises over $229 million with significant enterprise traction.
- 2015: Introduction of Splunk Cloud, moving core functionality to SaaS.
- 2018: Acquired Phantom for orchestration and automation capabilities.
- 2020: Splunk Observability Cloud unifies APM, infrastructure monitoring, and Synthetics.
- 2023: Cisco announces intent to acquire Splunk.
Heading into 2026, Splunk’s strategy centers on platform unification, AI-augmented experiences, and deep security integrations to secure and streamline digital transformation at scale.
Splunk Key Features
In 2026, Splunk continues to emphasize a unified platform across full-stack observability, enterprise security, and compliance. Its modular architecture allows businesses to adopt what they need and scale:
- Splunk Cloud Platform: Centralized log, metric, and event data processing for real-time infrastructure monitoring.
- Security Information and Event Management (SIEM): Threat detection, investigation, and response powered by Splunk Enterprise Security.
- Splunk SOAR: Automates workflows across security operations for faster incident resolution.
- Observability Suite: Includes APM, Infrastructure Monitoring, Real User Monitoring (RUM), and Synthetic Monitoring.
- Splunk AI Assistant (2025 Launch): Natural language queries, anomaly detection, and predictive alerts from integrated ML models.
Workflow & UX
Splunk balances power and usability across its web interface and mobile access. Most enterprise workflows begin with the intuitive search bar or pre-set dashboards:
- Custom Dashboards: Users can drag-and-drop data widgets and visualizations without scripting knowledge.
- Splunk Search Processing Language (SPL): Advanced users benefit from fast and flexible querying capabilities.
- AI Assistant: Helps formulate queries or debug dashboard components.
- User Roles: Built-in RBAC helps manage analyst, engineer, or admin privileges intuitively.
- Mobile & Edge UX: Updates let responders view alerts and reports in real time on mobile devices.
The UI has steadily improved after a 2023 redesign, now offering dark mode, animated charts, and context-sensitive sidebars.
Splunk Pricing Analysis & Value Metrics
Splunk employs usage-based pricing, which provides flexibility but requires diligent monitoring. Below is a simplified look at key pricing tiers in July 2026:
| Offering | Description | Starting Price |
|---|---|---|
| Splunk Cloud Platform | Data ingestion, storage, visualization | $150/month per GB (annual commitment) |
| Splunk Observability Cloud | APM, Infra, Synthetic Monitoring | $75/month per host |
| Splunk Enterprise Security | SIEM capabilities | Custom (avg. $25k+/yr) |
| Splunk SOAR | Workflow automation & security orchestration | From $10,000/yr |
| Splunk Synthetic Monitoring | API & Browser test simulations | $50/month per URL |
Value Overview: While pricing can scale high with data volume, most Fortune 1000 organizations view the stack as mission-critical. Mid-sized businesses using it selectively around security or observability benefit most when cost is monitored via quotas and anomaly budgeting tools.
Pro Tip: Splunk’s ingest-based pricing means setting data priorities upfront helps avoid surprise overages. Use sampling or filtering to optimize.
Competitive Landscape
Splunk’s hybrid-suite competes with diverse providers across security, observability, and full-stack monitoring:
| Product | Main Strength | Price Model | Best For |
|---|---|---|---|
| Splunk | Unified observability + security | Usage-based | Complex enterprises |
| Datadog | DevOps observability depth | Per-feature | SaaS and tech-first startups |
| Elastic Stack | Open-source freedom | Free with paid extras | Engineering-led SMBs |
| Sumo Logic | Ease + affordability | Flat-rate | SMBs |
| Microsoft Sentinel | Azure-native SIEM | Ingestion + storage costs | Azure-centric IT |
Use Cases
Common organizational use cases include:
- Enterprise Security Operations Centers (SOCs): Detecting lateral movement, orchestrating playbooks, integrating with firewalls.
- E-commerce Monitoring: Real-time website health, cart abandonment funnel tracking, CDN errors.
- Healthcare Compliance: HIPAA log retention and audit trails.
- Financial Services: Basel II risk profiling and anti-fraud pattern recognition.
- IOT Infrastructure: Ingesting device telemetry from remote sensors to monitor uptime, outages, or anomalies.
Integrations & Ecosystem
Splunk’s strength lies in its breadth of integrations, especially for enterprise-scale tooling:
- Cloud Platforms: AWS, Azure, GCP
- Identity & Access: Okta, Active Directory, Duo
- DevOps & CI/CD: GitLab, Jenkins, PagerDuty
- SaaS & Business Apps: Salesforce, ServiceNow, SAP
- Cloud-native Security: CrowdStrike, Palo Alto Prisma, Sysdig
The Splunkbase add-on marketplace features over 2,400 apps as of Q2 2025.
Pros & Cons
- Pros: Unified platform, industry-leading security analytics, AI-based anomaly detection, enterprise integrations, customizable dashboards
- Cons: Learning curve for SPL, expensive at high data volumes, configuration overhead for first-time users
Splunk FAQ
Is Splunk only for large enterprises?
No, Splunk offers scalable options for businesses of all sizes, though it's especially powerful for large-scale environments.
What is SPL in Splunk?
SPL stands for Search Processing Language — a straightforward query language for extracting insights from logs and metrics.
Does Splunk offer a free version?
Yes, Splunk Free allows limited ingestion and local deployment — great for small projects or evaluation.
What’s new in Splunk 2025?
Highlights include AI Assistant, new pricing controls, enhanced mobile alerts, and deeper support for sovereign cloud environments.
How secure is Splunk?
Splunk meets rigorous compliance (SOC 2, FedRAMP, ISO 27001) and supports role-based controls, encryption at rest, and audit trails.